This article is part of Qinsight’s cryptographic posture management use case series, connecting five security outcomes with practical operational workflows.
In brief
- Rotation is a dependency change. The producer can be updated while a consumer still expects the old material, so the plan needs both sides.
- Define the operation precisely (renewal, key rotation, trust-chain change or token-signing transition), map consumers and acceptance rules, and set an explicit overlap and retirement policy.
- Measure consumer verification coverage and the exceptions that keep old material active, and use before-and-after CBOMs as the change evidence.
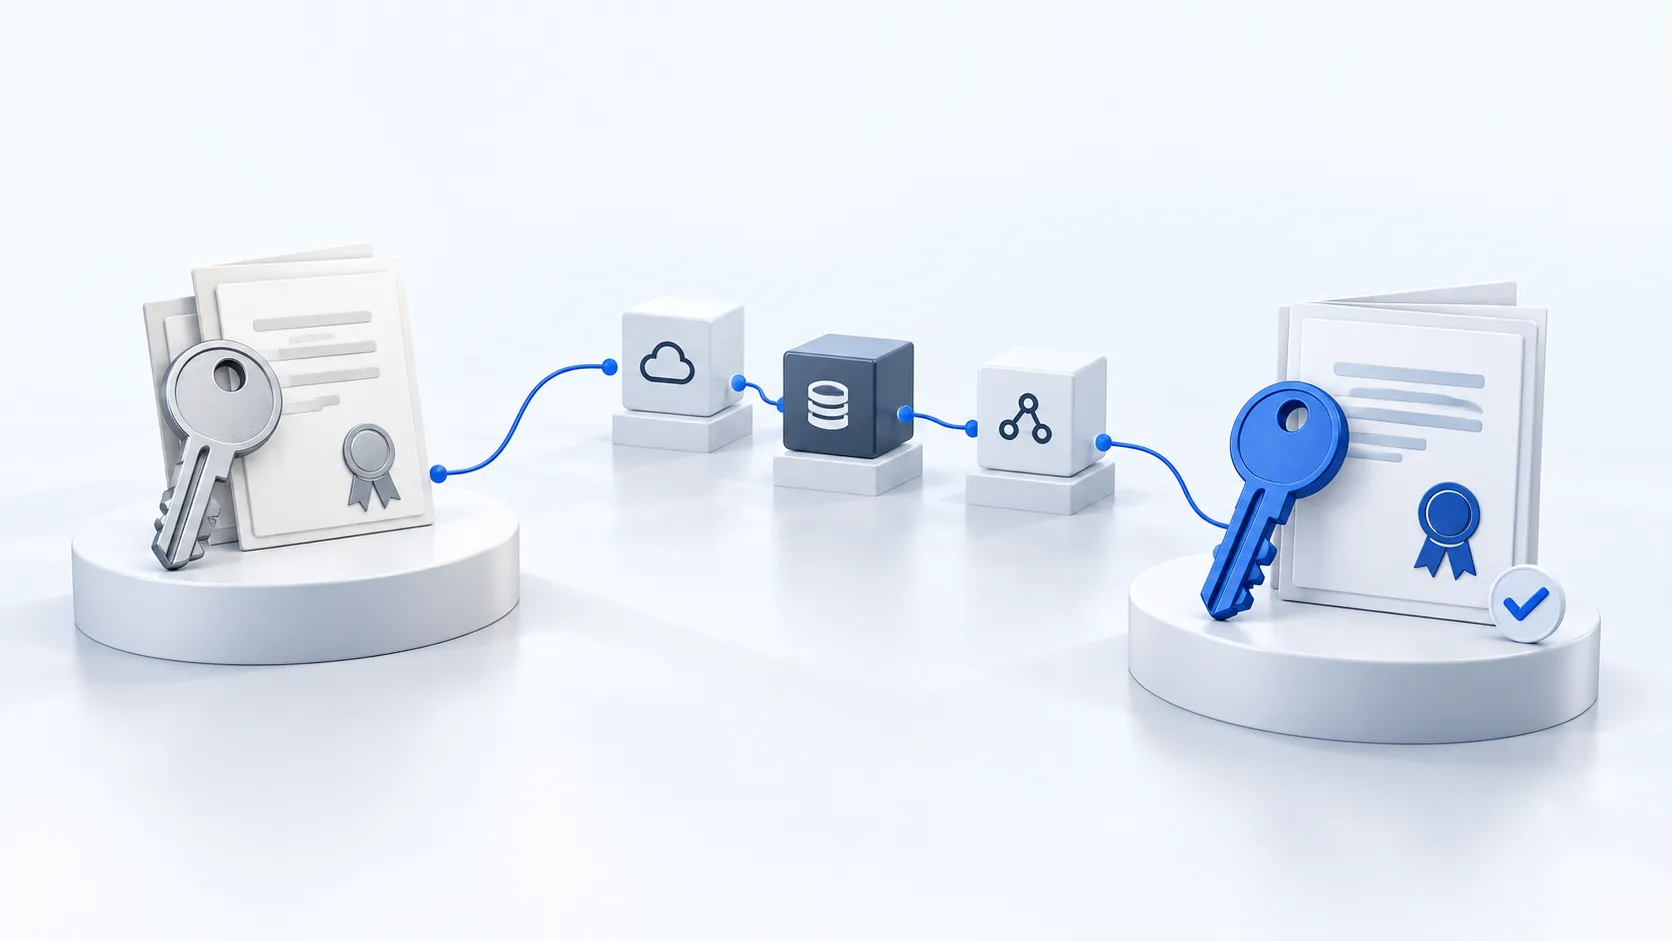
A key or certificate change can be technically correct and operationally incomplete. The new material is generated, but a consumer still trusts the old issuer. One application refreshes its configuration automatically while another needs a restart. A recovery environment retains the previous deployment.
For security leaders, the objective is to change cryptographic material while preserving the required security and service behavior. For architects, that means understanding the dependencies on both sides of the change and defining how each will be verified.
Cryptographic posture management supports this work by connecting keys, certificates, protocols and configurations to the systems that use them. That context helps a change team establish a realistic sequence, identify owners and decide when old material can be retired.
Define the change precisely
Certificate renewal, key rotation and trust-store changes are different operations. A renewed certificate may contain the same public key. Key rotation introduces new key material. Changing an issuing certificate authority, or CA, can require updates to relying systems even when the application’s hostname stays the same.
State the reason for the change as well. Routine lifecycle maintenance, an algorithm-policy change and a confirmed key compromise can require different timing and acceptance criteria. A planned overlap between old and new credentials may help continuity, while an incident may require a more immediate removal of trust.
The change record should name the cryptographic function, the object being replaced, the relevant environment and the intended end state. “Rotate the application certificate” leaves too much unspecified if the application uses separate certificates for inbound TLS, outbound mutual TLS and token signing.
Qinsight’s discussion of crypto-agility considers the wider ability to make cryptographic changes. A single rotation is a useful test of whether that ability exists in practice.
Identify producers, consumers and acceptance rules
Consider an illustrative business application that authenticates to a partner API using mutual TLS. The organization controls its client certificate and private key. The partner controls the authentication policy that accepts that client identity.
Replacing the local certificate is only one part of the change. The team needs to know whether the partner trusts an issuing CA, a particular certificate, a public key or an identity mapped from certificate fields. Each policy can create different coordination requirements.
Map the application instances that initiate the connection, including scheduled workers and recovery environments. Establish how each obtains the credential and when it reloads configuration. Ask the partner to confirm the acceptance criteria and the test connection that will demonstrate success.
The same principle applies to internal systems. A signer produces signatures; verifiers decide which signatures to trust. An encryption service protects data; consumers need access to the material required to decrypt it. A useful dependency map makes both roles explicit.
Use a rotation plan suited to the cryptographic function
| Change | Consumer dependency | Completion evidence |
|---|---|---|
| TLS certificate and private key | Client name validation, trust chain and any pinning. | Expected certificate presented; representative clients connect successfully. |
| Issuing CA or trust chain | Trust stores and supported validation paths. | Required clients accept the intended new chain. |
| Token-signing key | Verification-key distribution, caching and validation policy. | New tokens work; old-key acceptance follows the approved transition policy. |
| Data-encryption key | Data versions, wrapped keys, backups and decryptors. | New writes use the intended key; required historical reads remain possible. |
Managed key services add their own semantics. AWS KMS key rotation, for example, can replace material behind the same logical KMS key while retaining the material needed to decrypt older ciphertext. That operation does not automatically rotate generated data keys or re-encrypt the protected data.
This distinction matters when defining success. A rotation setting can demonstrate one lifecycle control while leaving a separate data-migration requirement outstanding. The plan should name the operation the system performs and the outcome the business needs.
Sequence the change around evidence
Begin with a current inventory of the producer and known consumers. Confirm ownership, refresh stale observations and agree which unassessed dependencies must be resolved before proceeding. Define the tests and recovery options before installing the replacement.
For a planned trust transition, prepare consumers to accept the new material where the protocol and policy permit it. Then deploy the replacement to the producers and check the intended behavior. The exact sequence depends on the system; some products manage rollover internally, while others require coordinated configuration changes.
Set an explicit overlap policy. State what can remain accepted, for how long and what evidence permits retirement. A transition window without an owner or end condition can leave old trust in place indefinitely.
Keep incident recovery separate from routine rollback assumptions. Returning to a compromised key can reintroduce the security problem that motivated the change. If normal rollback is unavailable, the team needs another continuity plan, such as controlled failover or a temporary service restriction.
Validate the paths the business actually uses
Test the ordinary transaction and the less frequent paths that matter: scheduled jobs, partner exchanges, secondary regions and disaster recovery. A successful browser connection may say little about a background client with its own trust store.
Record the expected object identifier, the consumer tested, the time of verification and the result. For short-lived workloads, include the deployment template or image that will create the next instance. Otherwise, a successful test of today’s instance can miss a configuration that returns during scale-out.
Retirement is a separate decision. Removing trust in an old signing key, revoking a certificate and deleting an encryption key have different consequences. AWS’s key-deletion guidance highlights the risk of making encrypted data unrecoverable and notes that KMS does not maintain a complete inventory of ciphertext protected by a key.
Check retention and recovery requirements with the data owner before destructive retirement. A quiet usage log does not establish that an archived dataset will never need the key again.
Use before-and-after CBOMs as change evidence
A cryptographic bill of materials, or CBOM, can capture the relevant estate before the change and after verification. Scope it to the application, workload or business service whose behavior the team is changing.
The starting snapshot should identify the key or certificate, its purpose, relevant protocol configuration, known consumers and supporting software. Link it to the current evidence, ownership records and unresolved dependencies. The resulting snapshot should identify the replacement and the observed deployment state.
Retain stable references so a reviewer can see which object changed and which relationships were revalidated. Distinguish an old key retained for a documented decryption requirement from an old credential that remains active by mistake.
As our guide to CBOMs and cryptographic inventories explains, the snapshot and maintained inventory have complementary roles. For change management, the useful artifact is a bounded record of the intended transition and the evidence supporting its completion.
How Atlas supports safer rotation planning
Atlas organizes the cryptographic inventory and connects it to available system context and dependencies. Teams can use that view to establish the proposed change boundary, identify the owners to involve and examine where the collected evidence remains incomplete.
Certificate managers, key-management services and deployment tooling execute their respective lifecycle actions. Atlas’s contribution is the context needed to plan and review those actions: what the object supports, which relationships need attention and what should be reassessed afterward.
Track the proportion of identified consumers validated, the time between deployment and verification, and the exceptions that keep old material in use. These measures help leaders distinguish a controlled transition from a change that remains partially complete.
A useful first exercise is one planned rotation with a manageable number of consumers. Document the acceptance criteria, perform the change through the existing operating process and compare the expected dependencies with those encountered. That gives the organization a concrete basis for improving its next rotation.
Explore the use case series
- Cryptographic posture management use cases
- Prevent certificate outages with service context
- Appliance exploits and cryptographic impact
- Exposed private keys and service impact
- Cryptographic library CVEs and service impact
- Build a CBOM for a critical business service
Related reading
- Cryptographic posture management use cases: Explore five security outcomes, 36 operational use cases and PQC migration.
- Crypto-agility and the growing gap between risk and response: Build the organizational ability to make cryptographic changes.
- 47-day TLS/SSL certificates: the operational impact of shorter lifecycles: Understand why frequent, reliable certificate changes matter.
Sources
- AWS KMS: Rotate AWS KMS keys: Key-material rotation, historical decryption and data-key limitations.
- AWS KMS: Delete an AWS KMS key: Retirement, ciphertext dependencies and recovery consequences.
Next step: Select one planned rotation and map its producers, consumers and acceptance tests. Work with Qinsight to define the discovery boundary.
Build the evidence behind the argument.
Start with one accredited boundary or one delivered system and produce evidence a reviewer will accept.